Financial crime
Add-on to Nucleus BankOSFour defenses. One investigation.
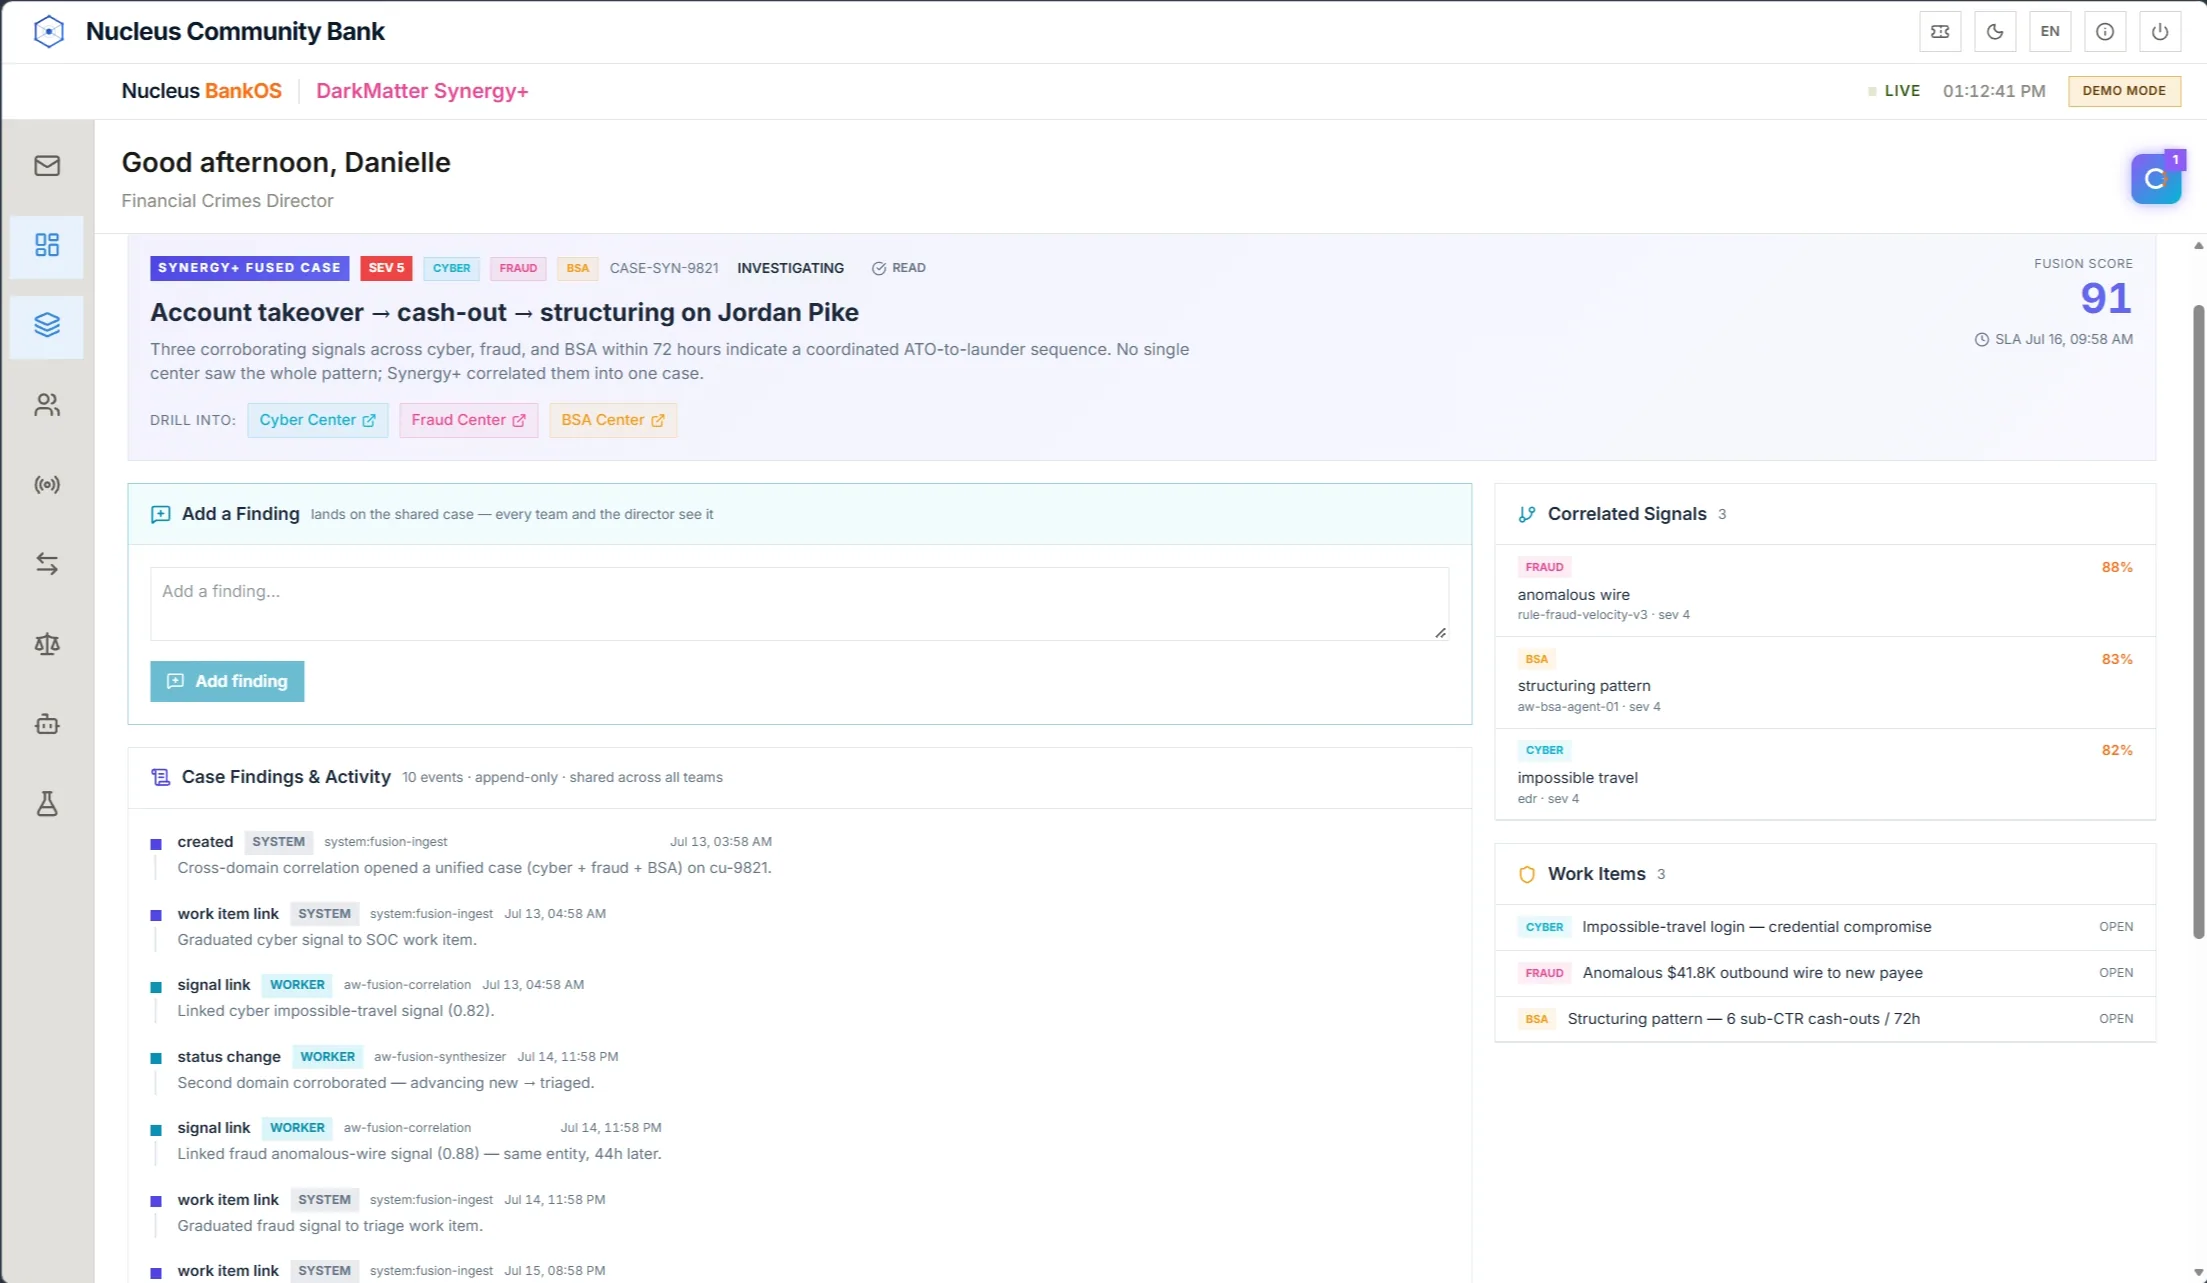
DarkMatter Synergy+ is an add-on to Nucleus BankOS that extends the DarkMatter fraud, cyber, BSA and compliance engines in every deployment into one fusion center. Signals correlate in real time into a single case file with one immutable log.
At a glance
- What it is
- Add-on extending the core’s DarkMatter
- Fuses
- Fraud, cyber, BSA/AML and compliance
- Detection
- Real-time on platform activity
- Case file
- One per investigation, shared by every team
- Thresholds
- Set by the bank, per rule, product and segment
- Log
- Immutable and replayable
- Device fingerprinting
- UEBA
- Insider threat
- SAR/CTR drafting
- Continuous KYC/KYB
- Risk scoring
- SIEM
What it adds
Financial crime is one network. Now the defense is too.
One case file across four teams
Fraud, cyber, BSA and compliance signals correlate into one entity graph and one case. No isolated queues, no batch handoffs.
From detection to response
Impossible travel, synthetic identities, impersonation scams and device spoofing are correlated across channels. Responses run at the thresholds the bank configured.
- Device fingerprinting and UEBA
- Insider-threat detection
- Impossible-travel and scam signals
Filings drafted, people decide
SAR and CTR narratives are drafted for analyst review from the case file. Synergy+ determines and records the required approval tier for each action.
Tuned to the bank’s risk appetite
Detection aggression is set per rule, product and segment. Synergy+ ingests the threat feeds the bank chooses and streams events to its SIEM.
Specifications
Capabilities
| Cyber | Device fingerprinting, UEBA, insider-threat and real-time threat detection |
|---|---|
| Fraud | Real-time transaction scoring; impersonation, scam and impossible-travel detection |
| BSA/AML | Typology detection, continuous KYC and KYB, customer risk scoring |
| Compliance | Risk coverage and enhanced reporting for oversight functions |
| Case file | One fused case and entity graph across all four domains |
|---|---|
| Filings | SAR and CTR narratives drafted for analyst review |
| Approvals | Required approval tier determined and recorded for each action |
| Audit | Every signal, decision and filing on an immutable, replayable log |
| Rules and thresholds | Configurable per rule, product and segment |
|---|---|
| Threat feeds | Ingests the sanctions, IP-reputation and device feeds the bank selects |
| SIEM | Streams events to the bank’s SIEM and takes signals back |
Questions
DarkMatter Synergy+: what banks ask
What is DarkMatter Synergy+?
DarkMatter Synergy+ is an add-on to Nucleus BankOS that fuses fraud, cyber, BSA and compliance into one real-time investigation. It extends the DarkMatter engines already included in every deployment.
How is it different from the DarkMatter in the core?
Every deployment includes DarkMatter’s fraud, cyber, BSA and compliance engines on one identity and audit log. Synergy+ adds the fusion layer: correlated signals, one shared case file and an entity graph across all four.
Does Synergy+ file SARs automatically?
No. It drafts SAR and CTR narratives from the case file for analyst review, and a person decides what is filed.
Who sets detection thresholds?
The bank. Sensitivity is configurable per rule, product and customer segment, so it can tighten high-risk flows and loosen where friction costs customers.
Does it work with our existing security tools?
Yes. Synergy+ streams events to the bank’s SIEM, takes signals back, and ingests the threat feeds the bank chooses.
Is monitoring real-time in side-core deployments?
For activity that flows through Nucleus BankOS, yes. Activity still settled on an incumbent core is analyzed on synced data, near-real-time rather than instantaneous.
Bring the workflow you want to change.
A working session with the founders on your use case, your core and your first step.